Release Notes 2025- June
Outline
Release v4.1.108
June 30, 2025
1. Custom Field-Based Widgets for Third-Party Dashboards
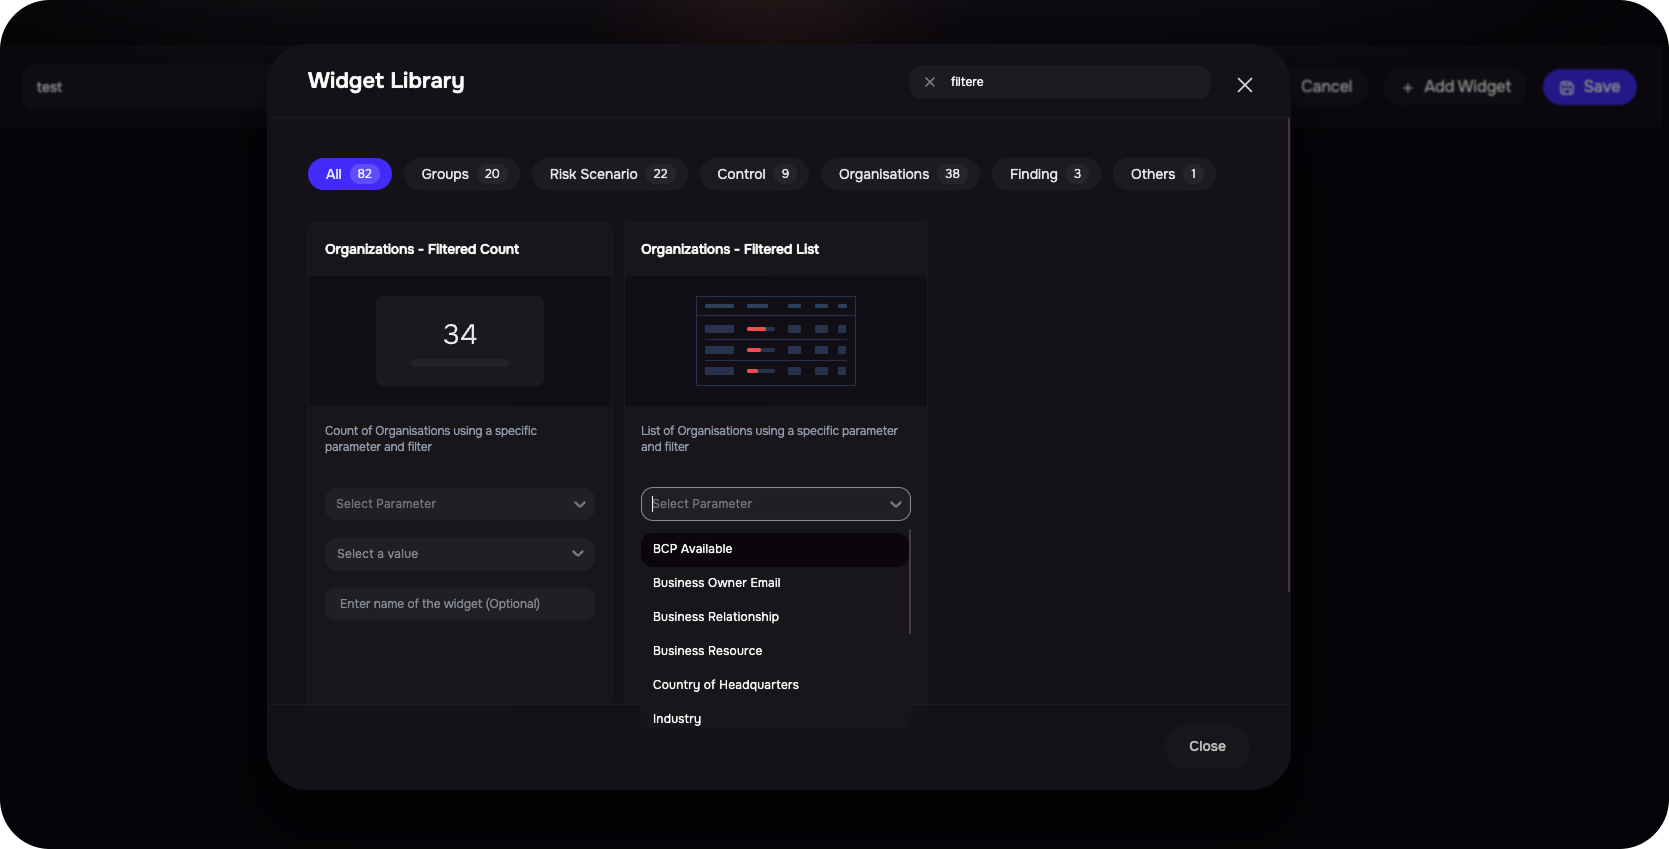
We’re introducing custom field-based widgets for Third-Party dashboards. With widgets like Filtered List, Filtered Count, and Distribution, users can now build highly tailored visualizations using custom fields. This enables flexible reporting across geographies, business units, regulatory categories, and more.
2. Improved Loss Exceedance Curve
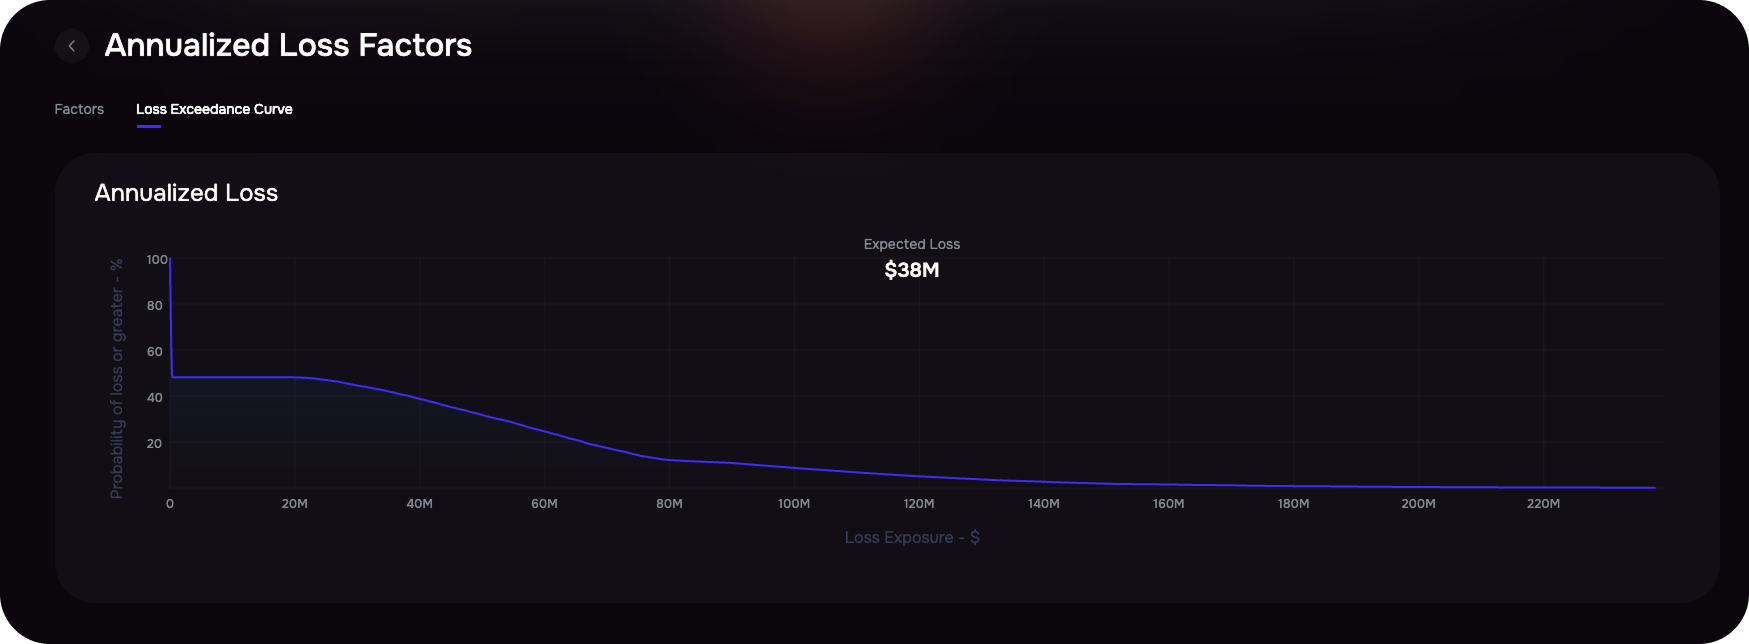
The Loss Exceedance Curve now uses a significantly higher number of data points, resulting in a smoother and more realistic view of potential losses. This enhancement resolves earlier long-tail distortion issues and delivers deeper insights for advanced risk analysis.
3. Enhanced Risk Drill-Down Experience
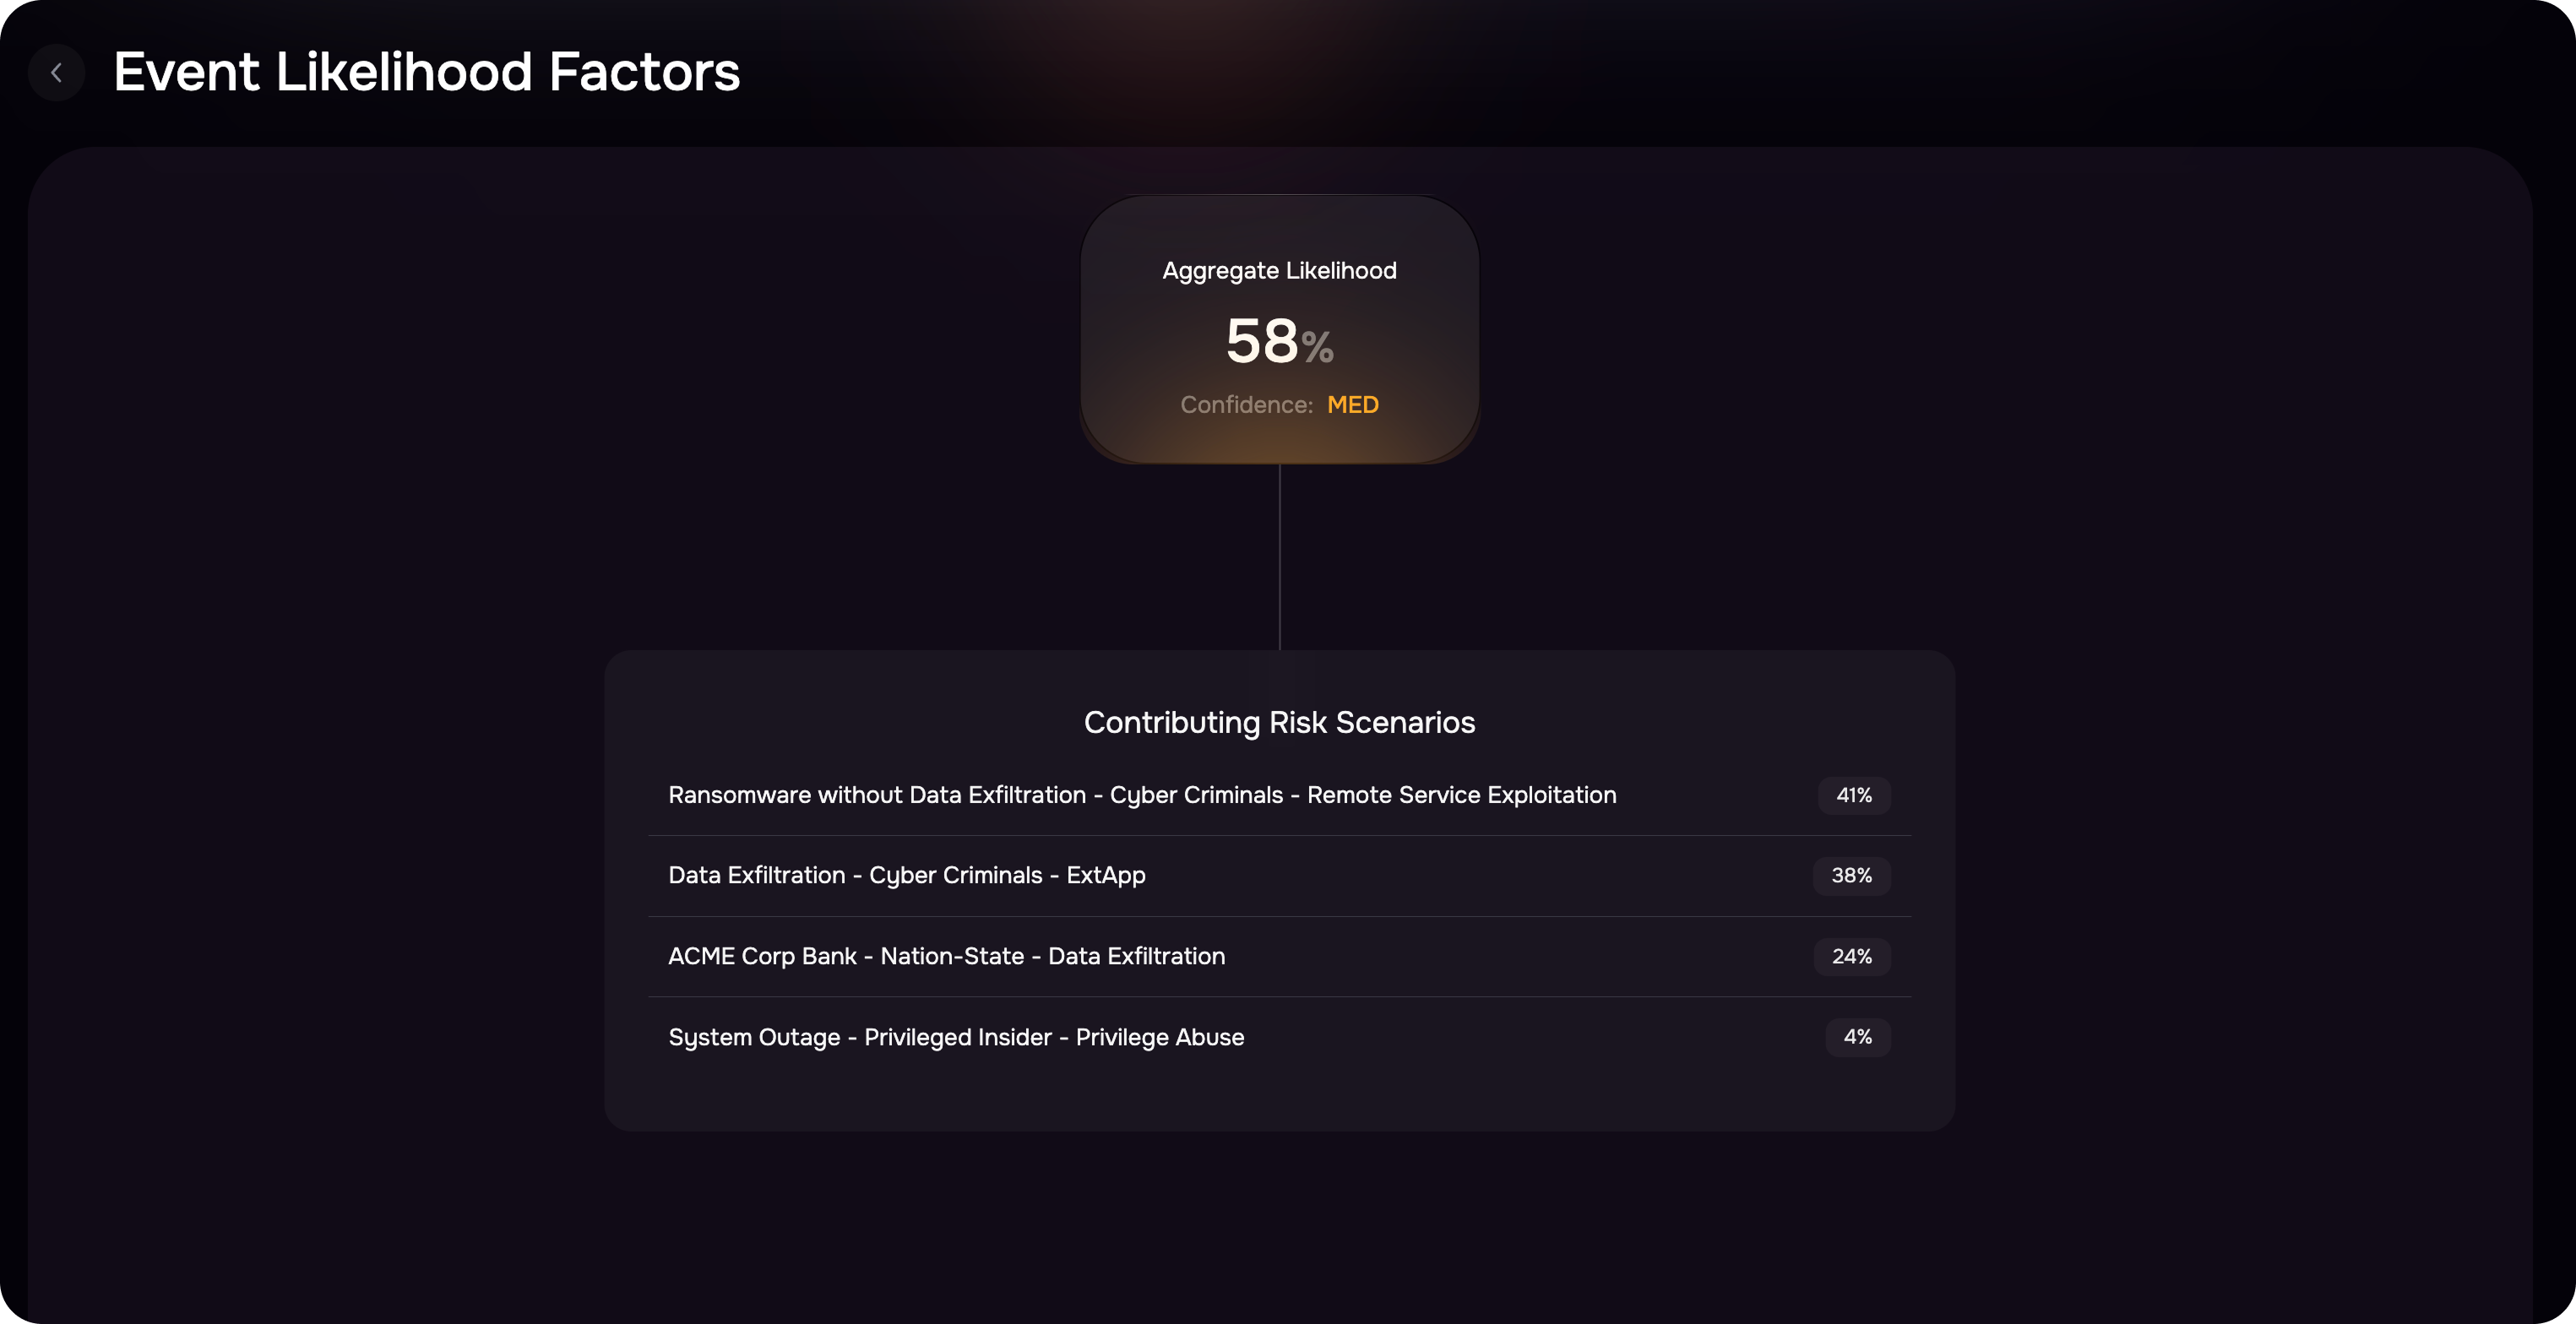
You can now click on Aggregate Likelihood and Aggregate Loss numbers to see detailed scenario-level data across all groups. For example, clicking on Likelihood shows all the distributions contributing to the overall value.
4. Enhanced Visibility in “See What Changed” for Risk Scenarios (Early Access)
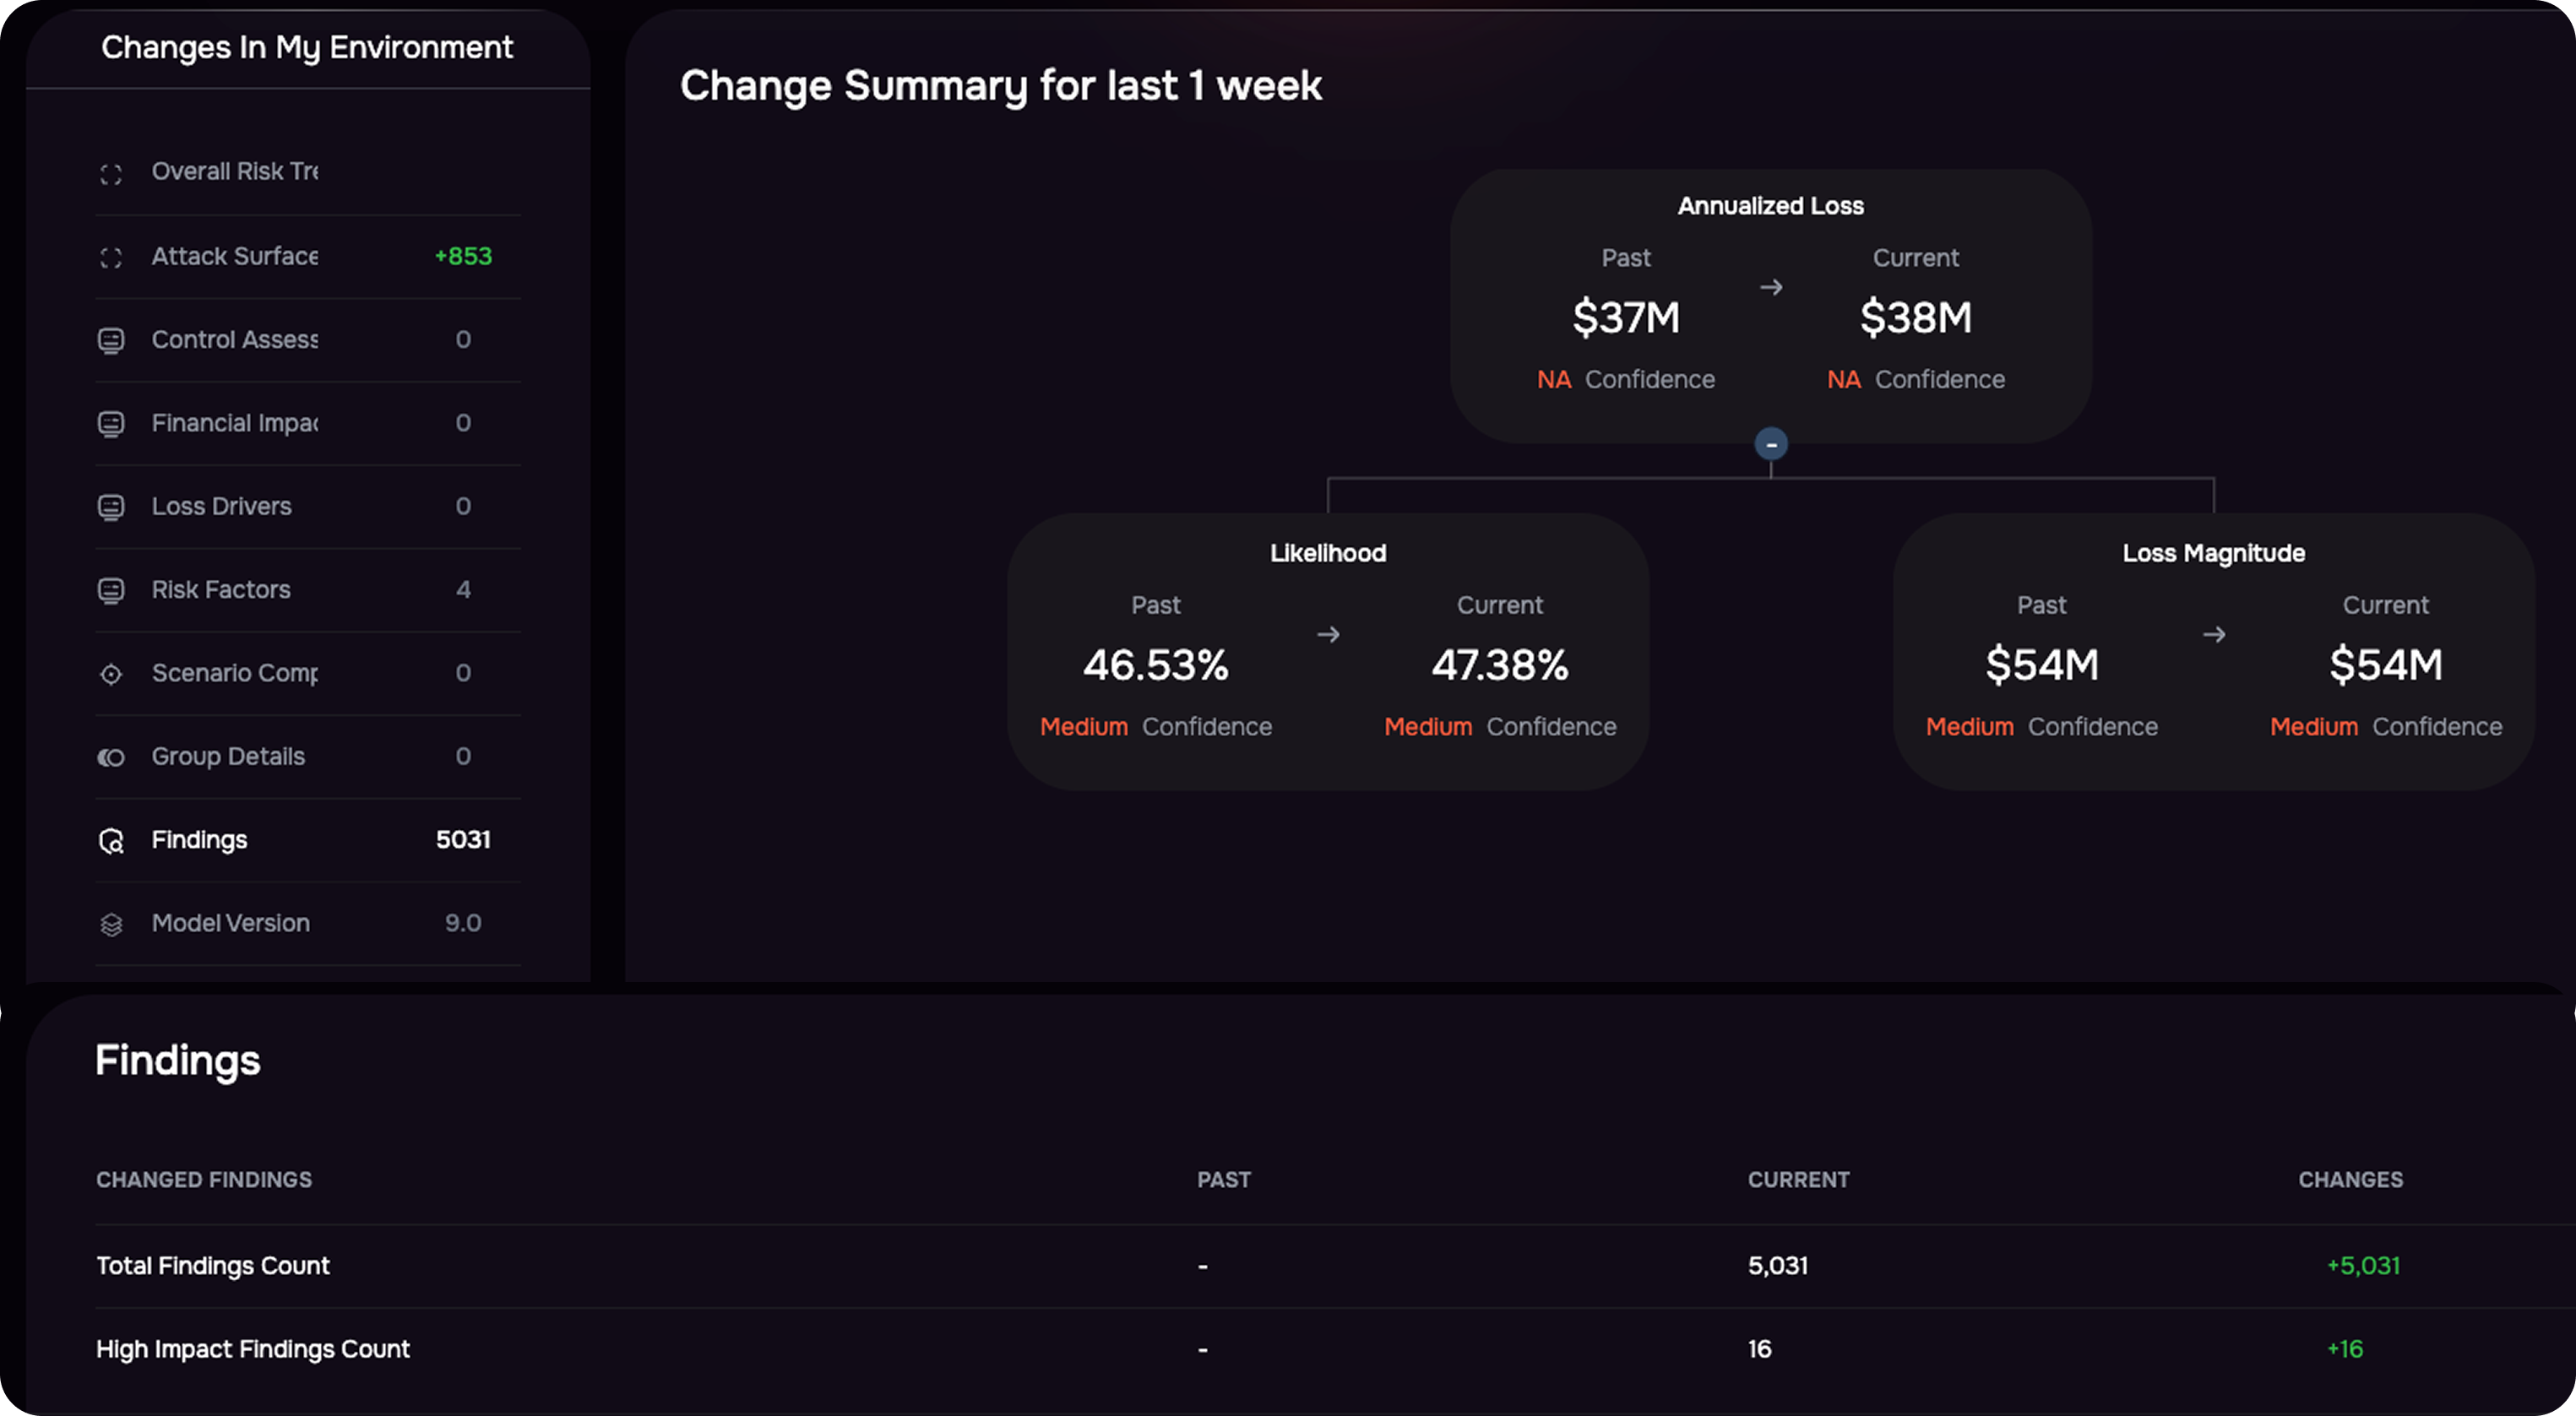
We've improved the “See What Changed” section to include counts of changing Findings, High Impact Findings (HIF), and changes in Loss Event Frequency (LEF). These updates provide deeper context into what’s driving risk changes, improving transparency and supporting better decision-making.
5. Threat Intel Updates
356 security incidents added in the library for third-party breach notifications.
38 new CVEs are marked as Exploitable.
160 new Threat Events added to the Threat Center.
Release v4.1.107
June 16, 2025
1. Introducing Finding Center
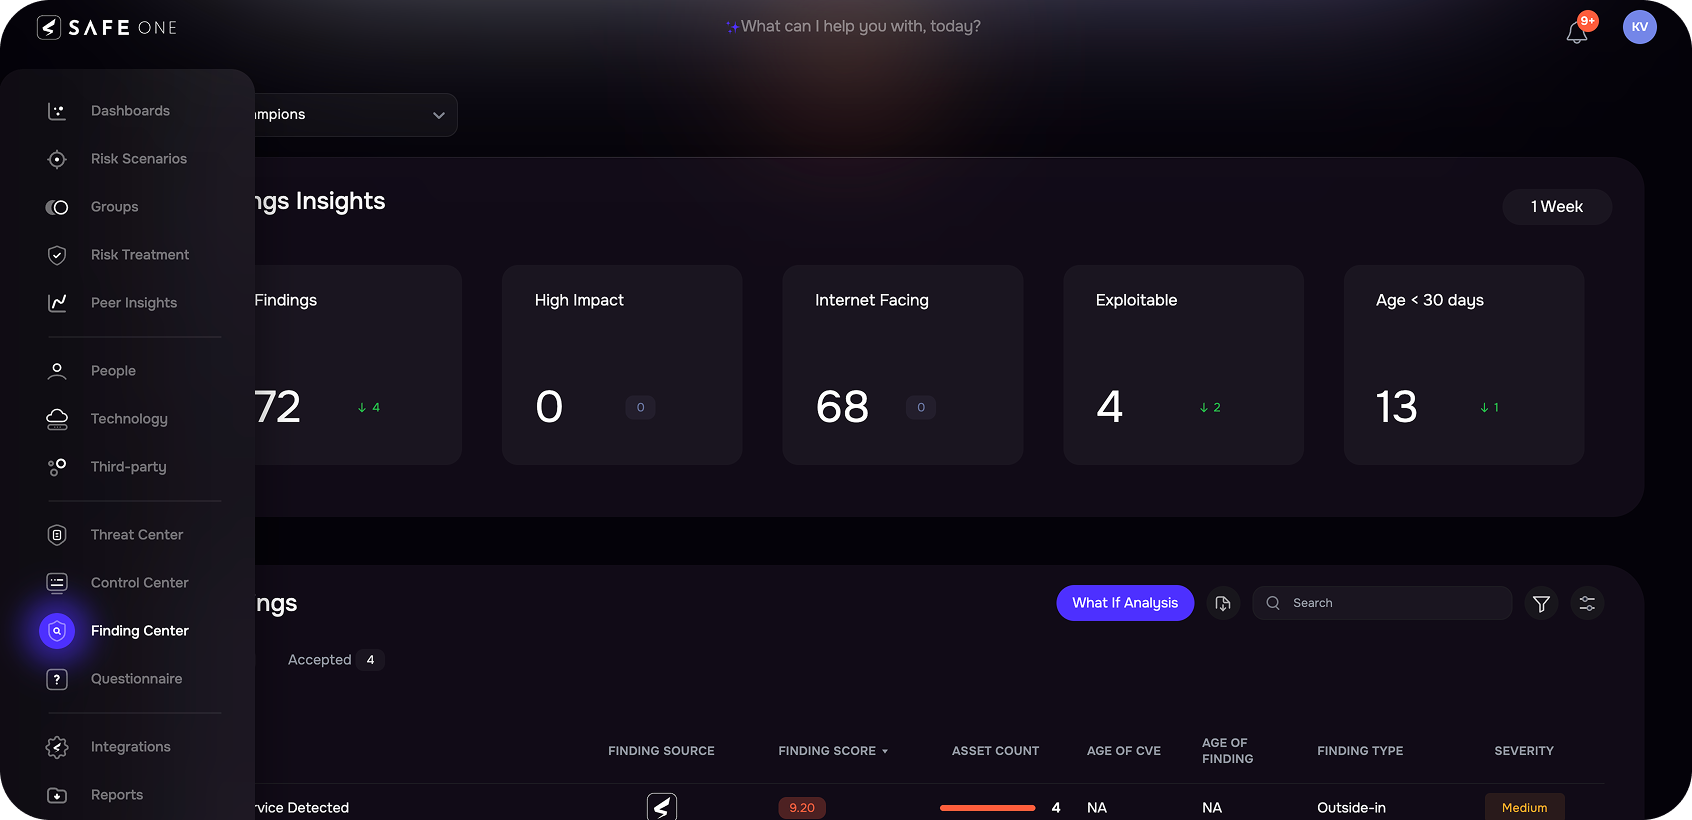
The new Finding Center provides a centralized hub for managing all findings, and it is now accessible directly from the left navigation.
Includes a built-in Group Selector, enabling quick group switching without navigating away.
Enables users to perform What-If Analysis directly from the Findings page.
Supports operations like filtering findings, exporting results, and more.
2. Accept Findings with Reasons and Expiry Controls
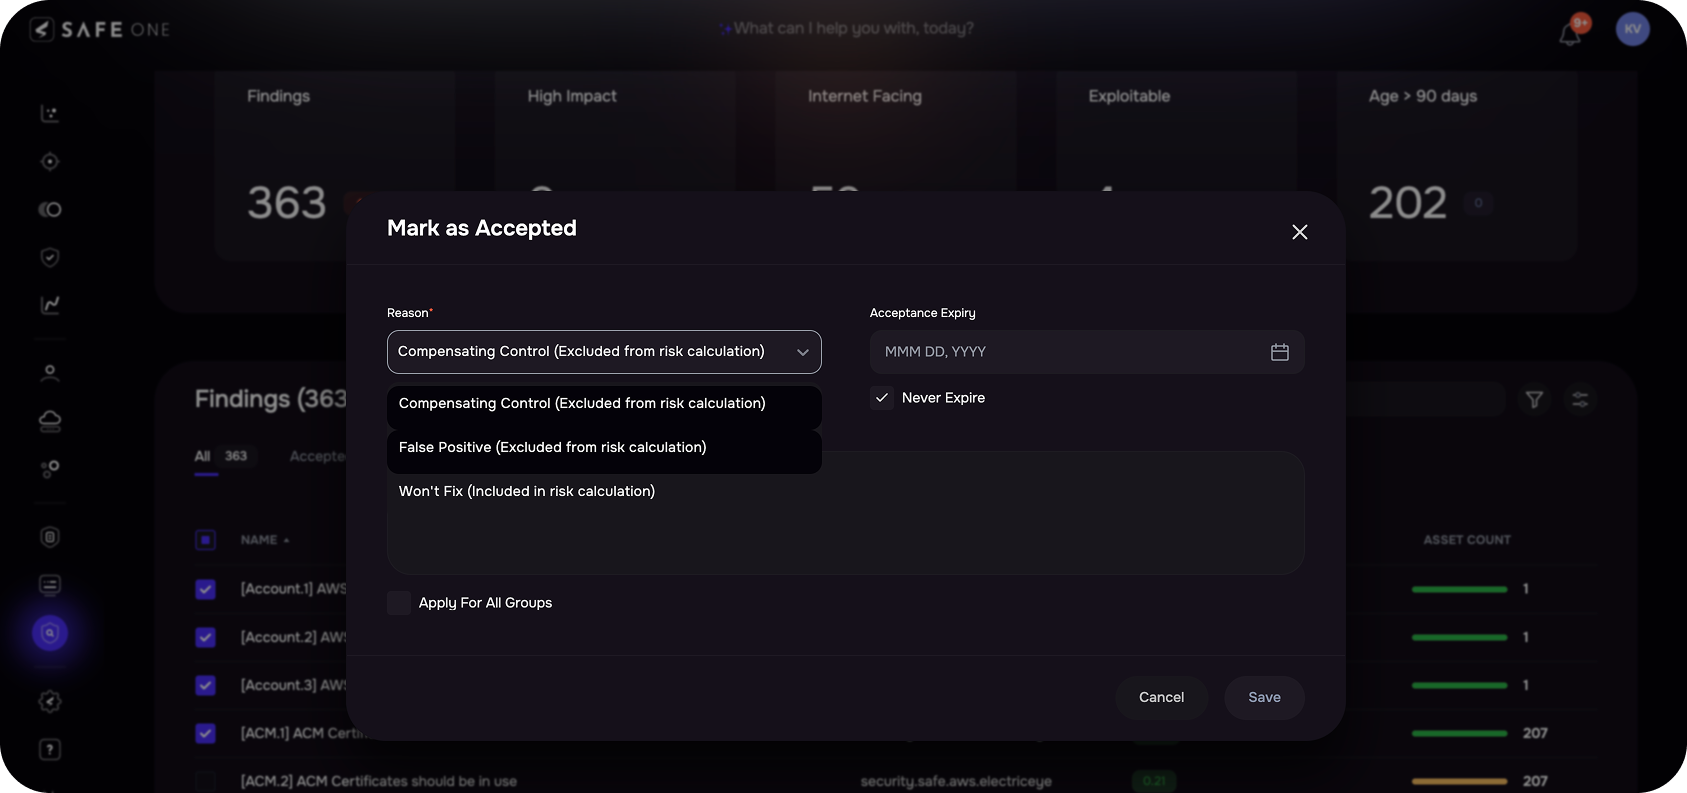
You can now mark individual or bulk findings as “Accepted” with clear reasoning, expiry, and full visibility across SAFE.
Choose from three reasons (Compensating Controls, False Positive, Won’t Fix) with a mandatory rationale and optional expiry.
Accepted findings can be filtered and viewed by reason and expiry in the Findings list.
Status can be reset anytime, and all actions are captured in the audit log for traceability.
Note: Accept Findings is currently available only for first-party findings. Support for accepting third-party findings is not available at this time.
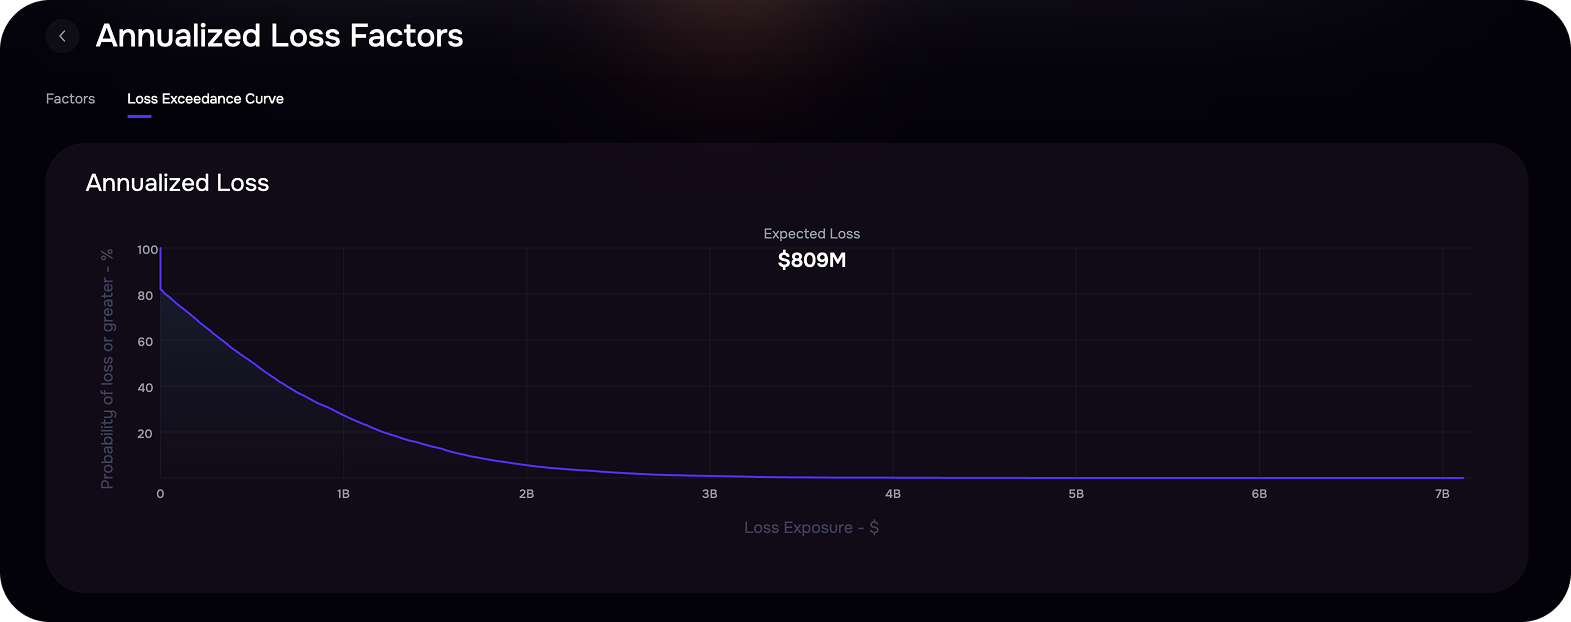
3. Loss Exceedance Curve at Aggregate Level (Early Access)
The Loss Exceedance Curve is now available at the aggregate level, offering a broader view of risk exposure across groups. The previously static Annualized Loss card is now clickable, allowing users to access detailed loss analysis. Both Loss Factors and the LEC are displayed at the group level, enabling more informed, organization-wide risk assessments.
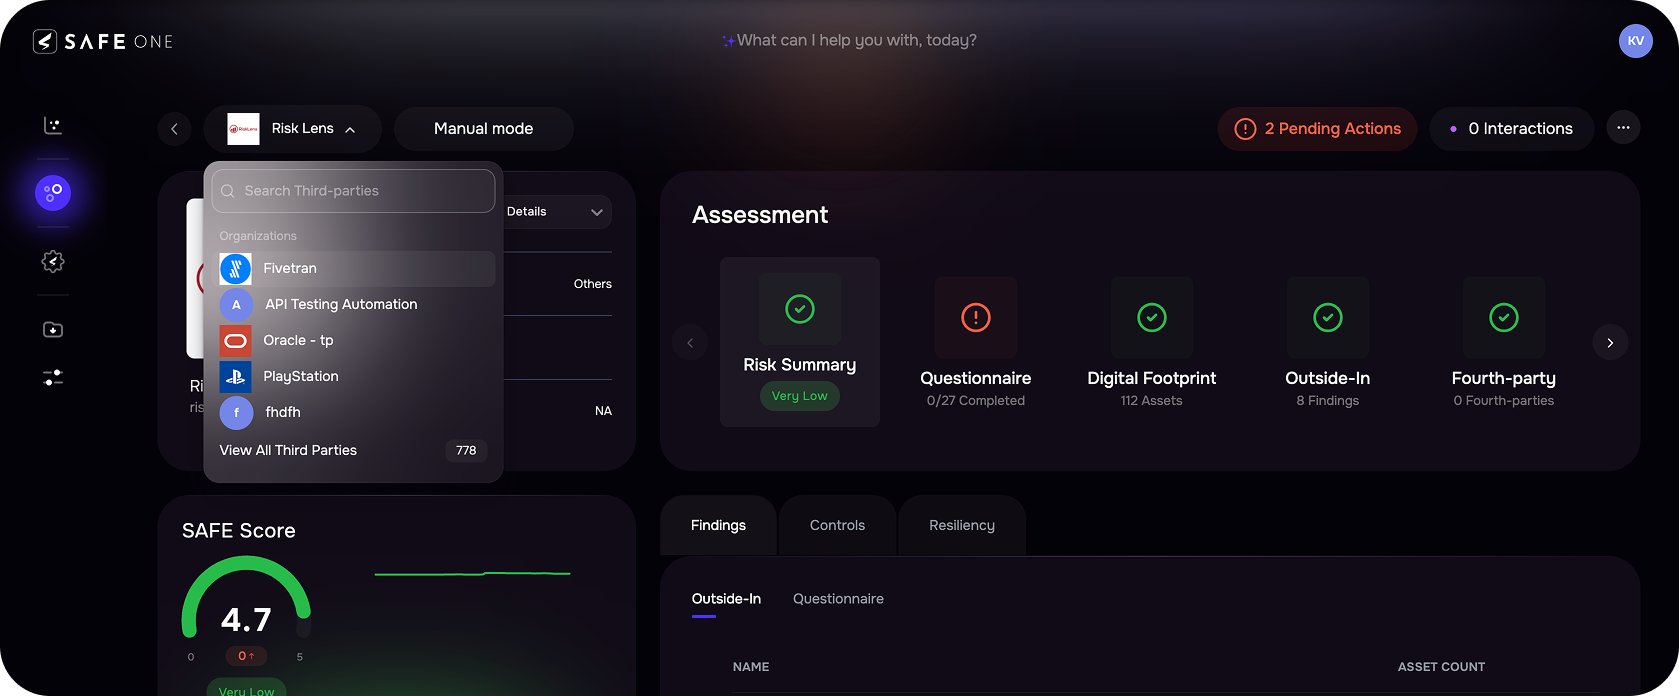
4. Seamless Third-Party Navigation with New Switcher
The Third-Party details page now includes a switcher that allows users to easily search and switch between third-party organizations without returning to the main list. By default, the switcher displays organizations sorted by their last updated time, and users can quickly search by name to jump directly to a specific profile.
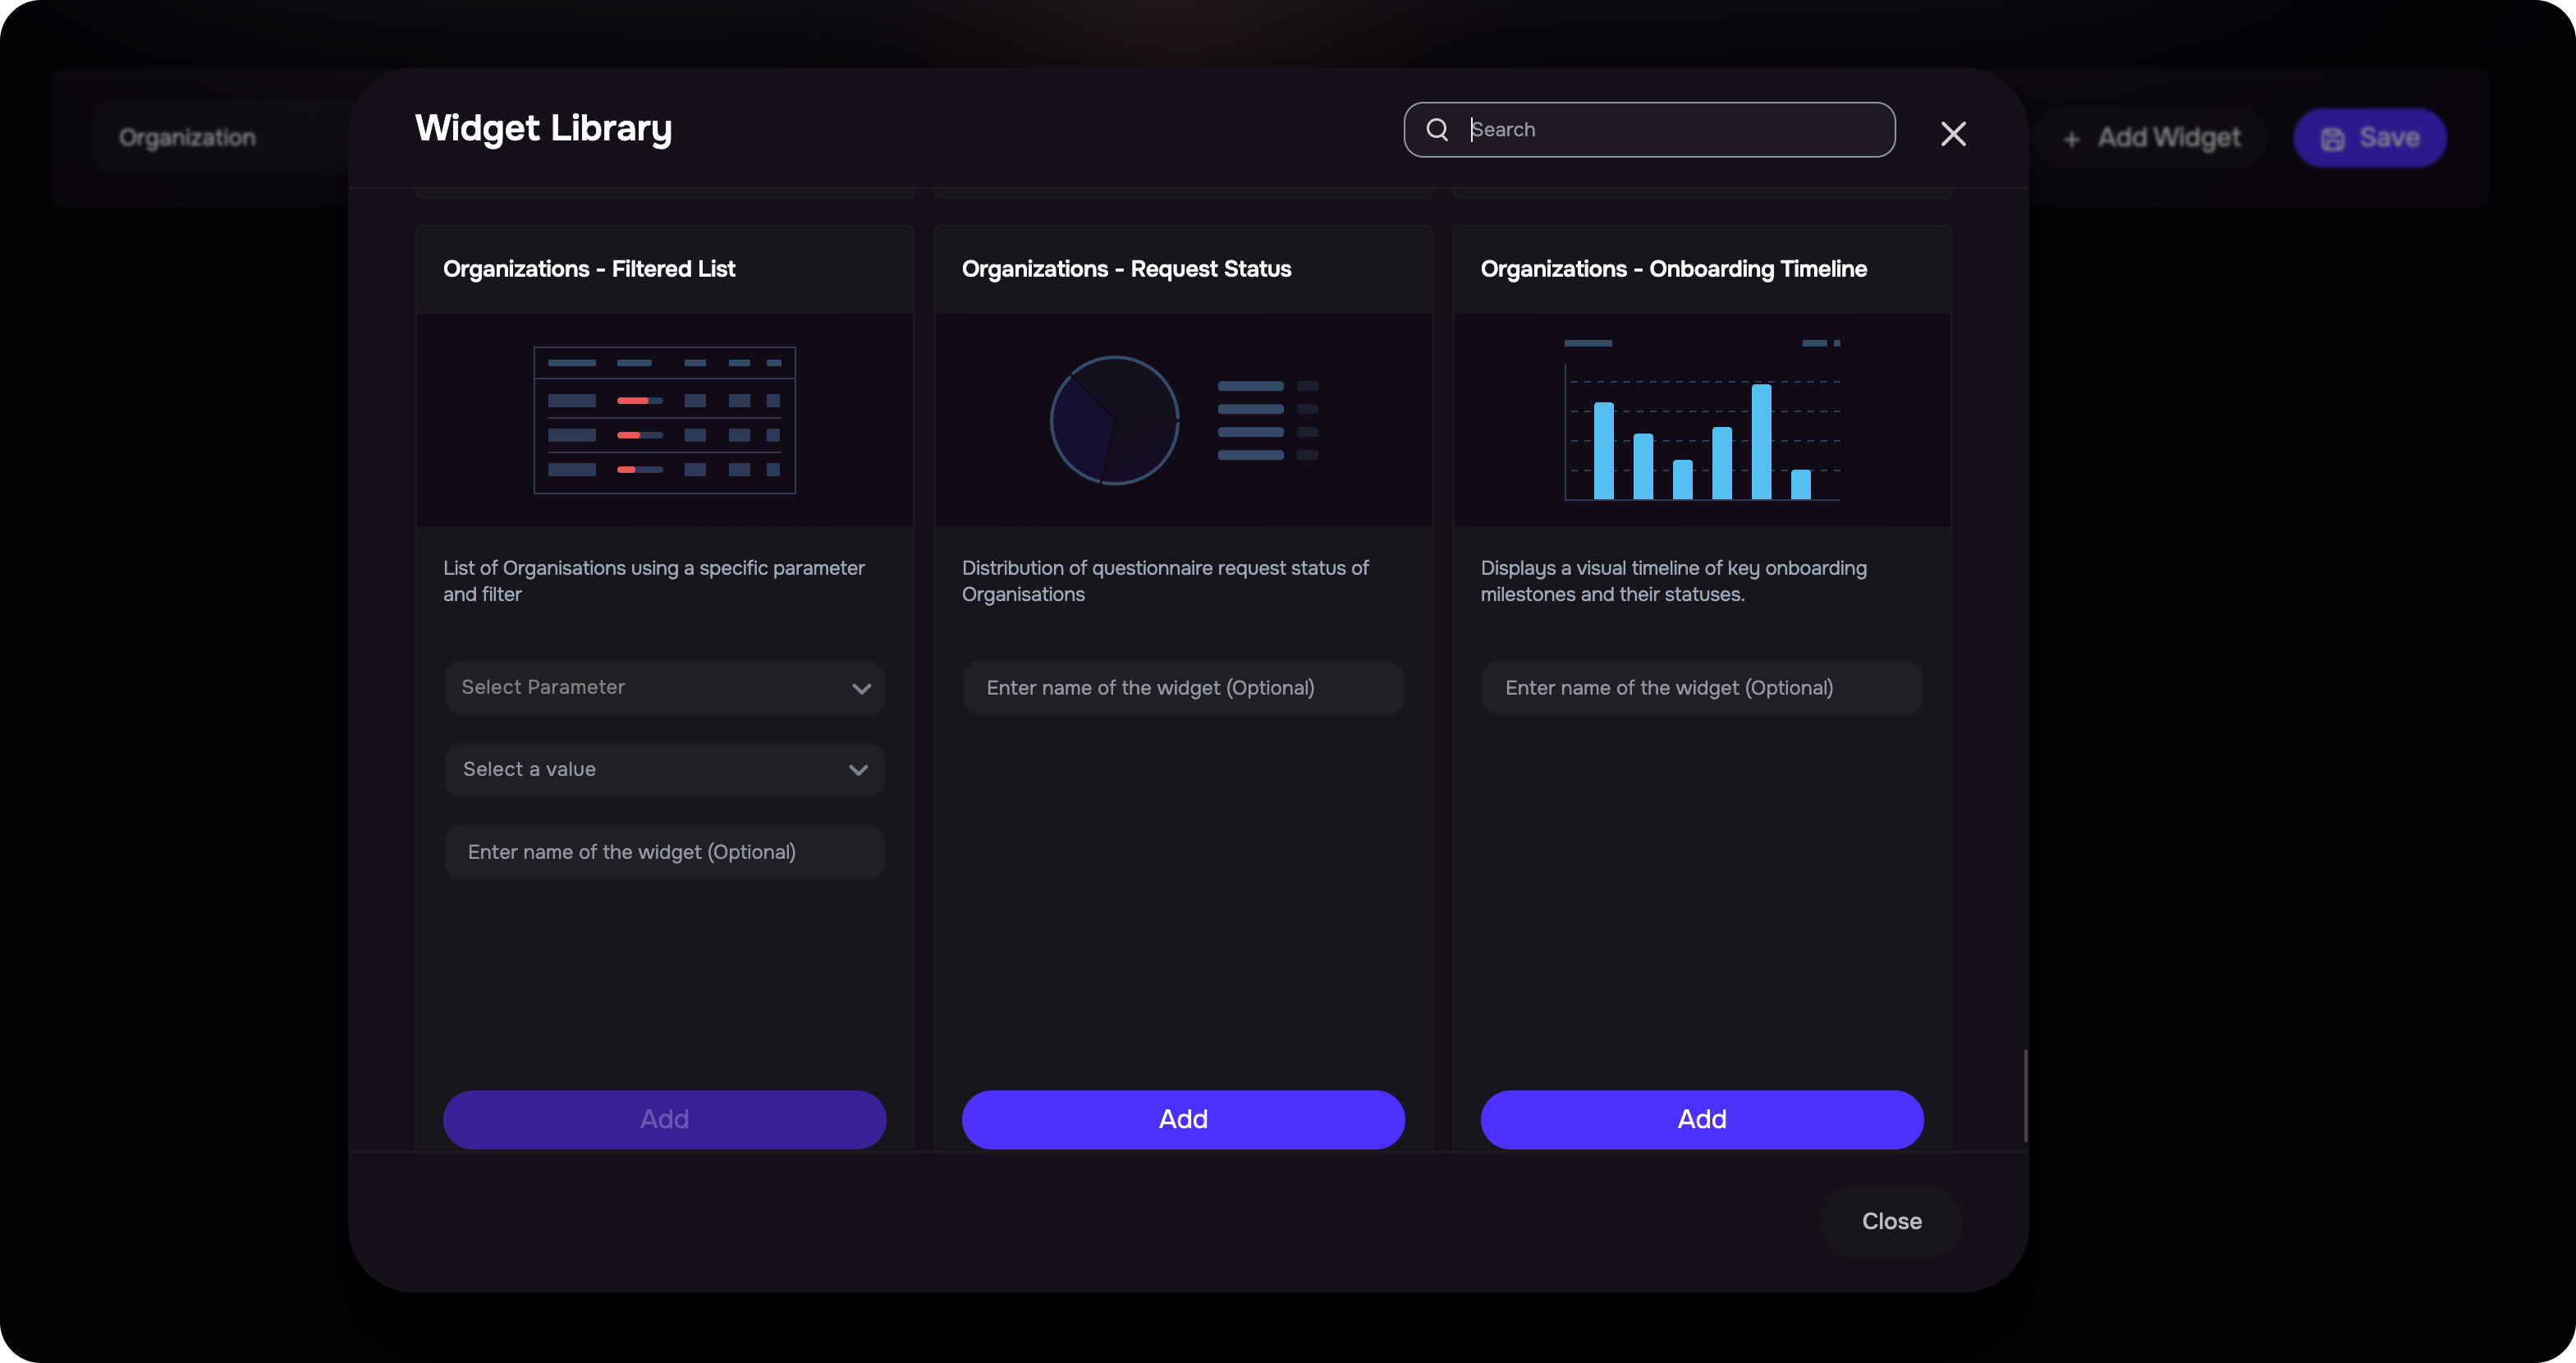
5. New Dashboard Widgets for Organizational Insights
We’ve introduced a comprehensive set of dashboard widgets to provide deeper visibility into third-party risk metrics. These include onboarding timelines, distribution views with multiple chart types, request status summaries, and quick inventory search. All widgets support flexible sizing, filtering, sorting, and the ability to add multiple instances for tailored insights.
6. Enhancements in ServiceNow Asset Connector
We have enhanced the ServiceNow Asset Connector to offer improved configurability, a better user experience, and compatibility with the latest ServiceNow Yokohama release.
7. Threat Intel Updates
322 security incidents added in the library for third-party breach notifications.
46 new CVEs are marked as Exploitable.
140 new Threat Events added to the Threat Center.
8. Other Enhancements
Enhanced Tanium integration to support ingestion of Cloud Instance Tags for improved asset context and tagging accuracy.
Added on-demand API to export complete Monte Carlo simulation data for the Loss Magnitude of a given risk scenario, including Single Loss Expectancy (SLE).
Did this article help?
Let us know by leaving a star rating at the top of this article.